

FedRAMP • GovRAMP • CMMC • DoD • AI • Privacy
The Only IA / 3PAO that's
Advisory-Only. Engineer-First. CLI-Comfortable. Actually Technical. DevSecOps-Native. Customer-Obsessed. Automation-First. Built for 20x. Absurdly Technical.
bladestack.io is a FedRAMP-recognized advisory-only 3PAO and Marketplace-listed advisor.
We provide advisory services, not independent assessments. Our architects and engineers embed with your team to make FedRAMP Certification feel like engineering, not paperwork. Agency authorization remains a separate decision.
Independent advice.
Independent assessment.
Advisory and independent assessment serve different purposes. The rules protect impartiality; our advisory-only model makes the separation clear.
Impartiality is required
Accredited assessment bodies must meet applicable ISO/IEC 17020 impartiality requirements and FedRAMP restrictions on assessing work they helped develop. A corporate structure alone does not establish independence.
The two-year lookback
A2LA R311 restricts assessment of systems consulted on within the preceding two years. Assessor-owned tools that directly support a provider can count as consulting; affiliated-company tools require specific impartiality review and approvals.
Separation under CR26
FedRAMP prohibits assessing the same cloud service offering within two years after advisory or consulting services, subject to any expressly published scoped exception. The service performed determines the role.
Compare two illustrative service models. Ask who advises, who assesses, how impartiality is documented, and whether prior services affect assessor eligibility.
Where a group offers both services, confirm applicable impartiality safeguards, prior consulting relationships, and assessor eligibility. A shared brand or separate legal entity does not answer those questions by itself.
When the proposal changes,
ask who does the work.
An advisory offer can follow an unsuccessful assessment proposal. Use this illustrative conversation to ask about engineering capability, service scope, and the effect on future assessor eligibility.
Press play. This fictional example highlights questions to ask when an assessment proposal becomes an advisory proposal.
Evaluate the team, the implementation scope, and the independence arrangements. Advisory is our focus from the first conversation.
The bladestack.io Difference
Why we're fundamentally different
Three commitments that define how we work: exclusive advisory focus, engineering depth, and security outcomes.
Advisory-Only Independent Assessor/3PAO
A FedRAMP-recognized advisory-only 3PAO and Marketplace-listed advisor. We focus exclusively on advisory work and do not independently assess the systems we help build. Your success is our focus.
Engineer-First DNA
Not auditors who learned cloud; engineers who learned compliance. We don't hire technical writers or desk jockeys. Our cyber-samurais are architects, SREs, and engineers equally comfortable in your CI/CD pipeline and the boardroom.
No "Check-the-Box"
Compliance without security is a liability. We solve hard engineering problems to build a security posture that is a genuine asset, not a line item.
The rules are structured.
The work is engineering.
FedRAMP’s Consolidated Rules for 2026 (CR26) publish structured definitions, requirements, and Key Security Indicators. We connect that rulebook to your architecture, implementation, and evidence. Our work supports FedRAMP 20x certification and Rev5 modernization, including Certification Package Overviews, Security Decision Records, and the artifacts required by your certification profile and transition schedule. Automation makes evidence easier to maintain; engineering judgment makes it useful. Probe the stack for the work at each layer.
Ask what happens below L4. Who reviews the architecture, opens the pull request, investigates a failed check, and explains the evidence? Under both Rev5 and 20x, documentation needs to reflect the implemented service. We bring the engineering depth to connect those layers and help your team maintain a defensible certification package.
Start Here
Gap Analysis/Discovery
Before you spend a dollar on remediation, know exactly where you stand. We identify what is blocking your path to FedRAMP Certification and build a technical roadmap tailored to your architecture.
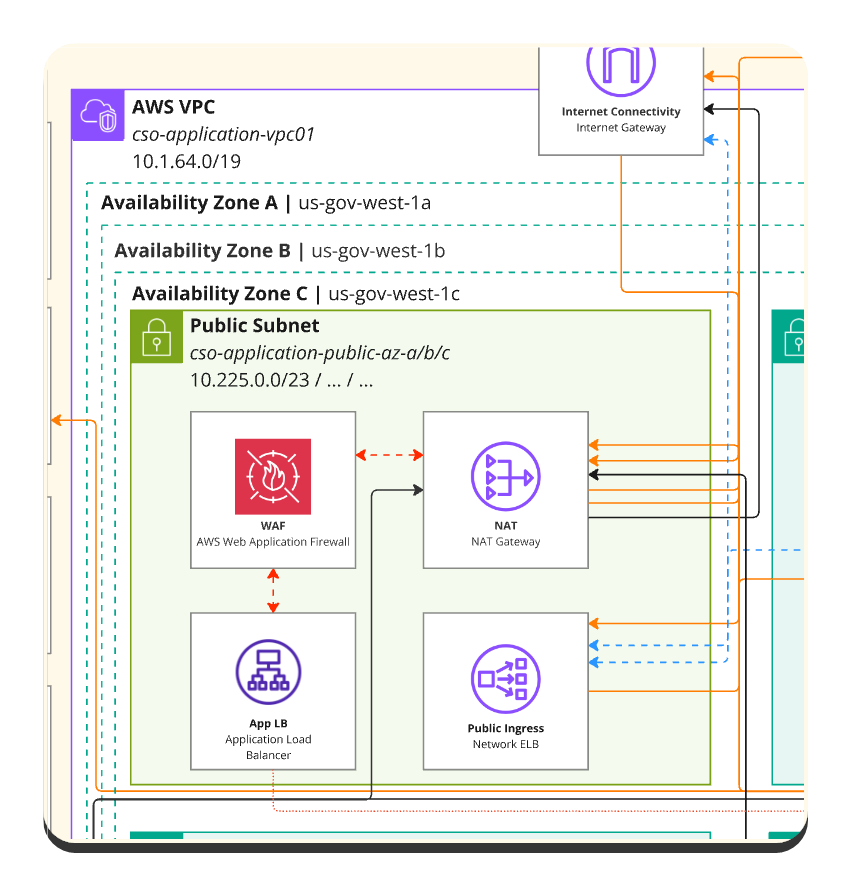
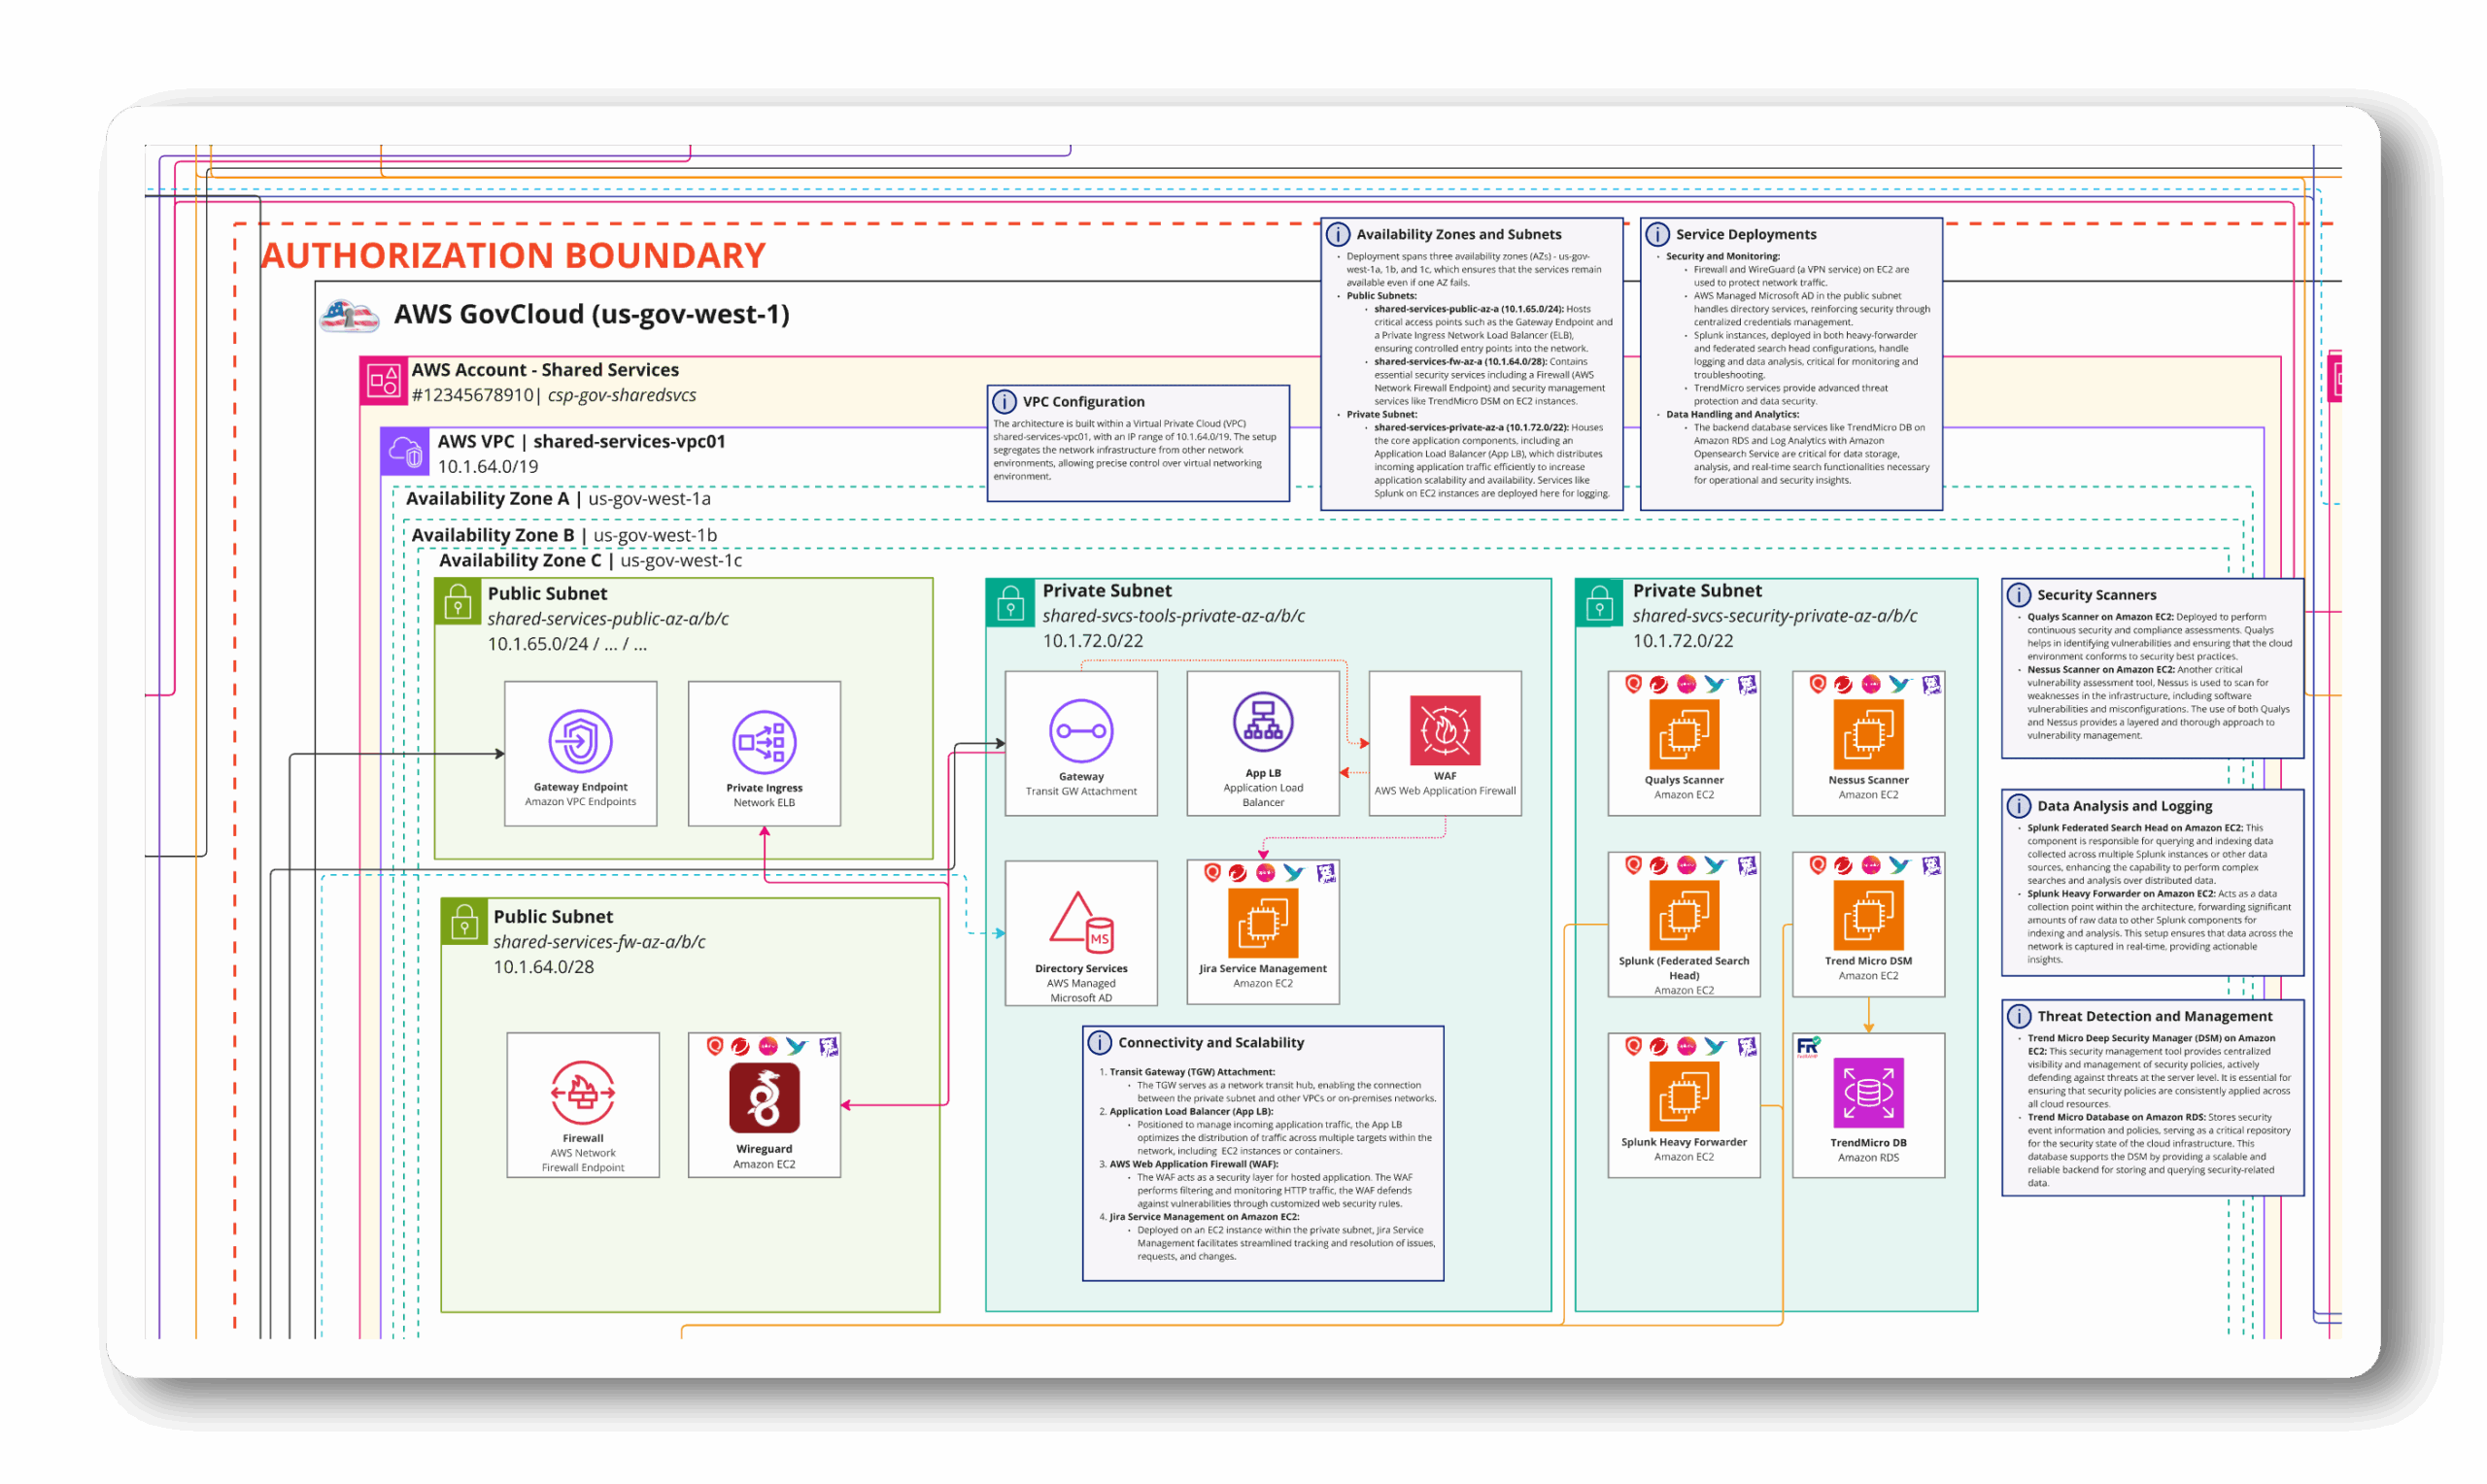
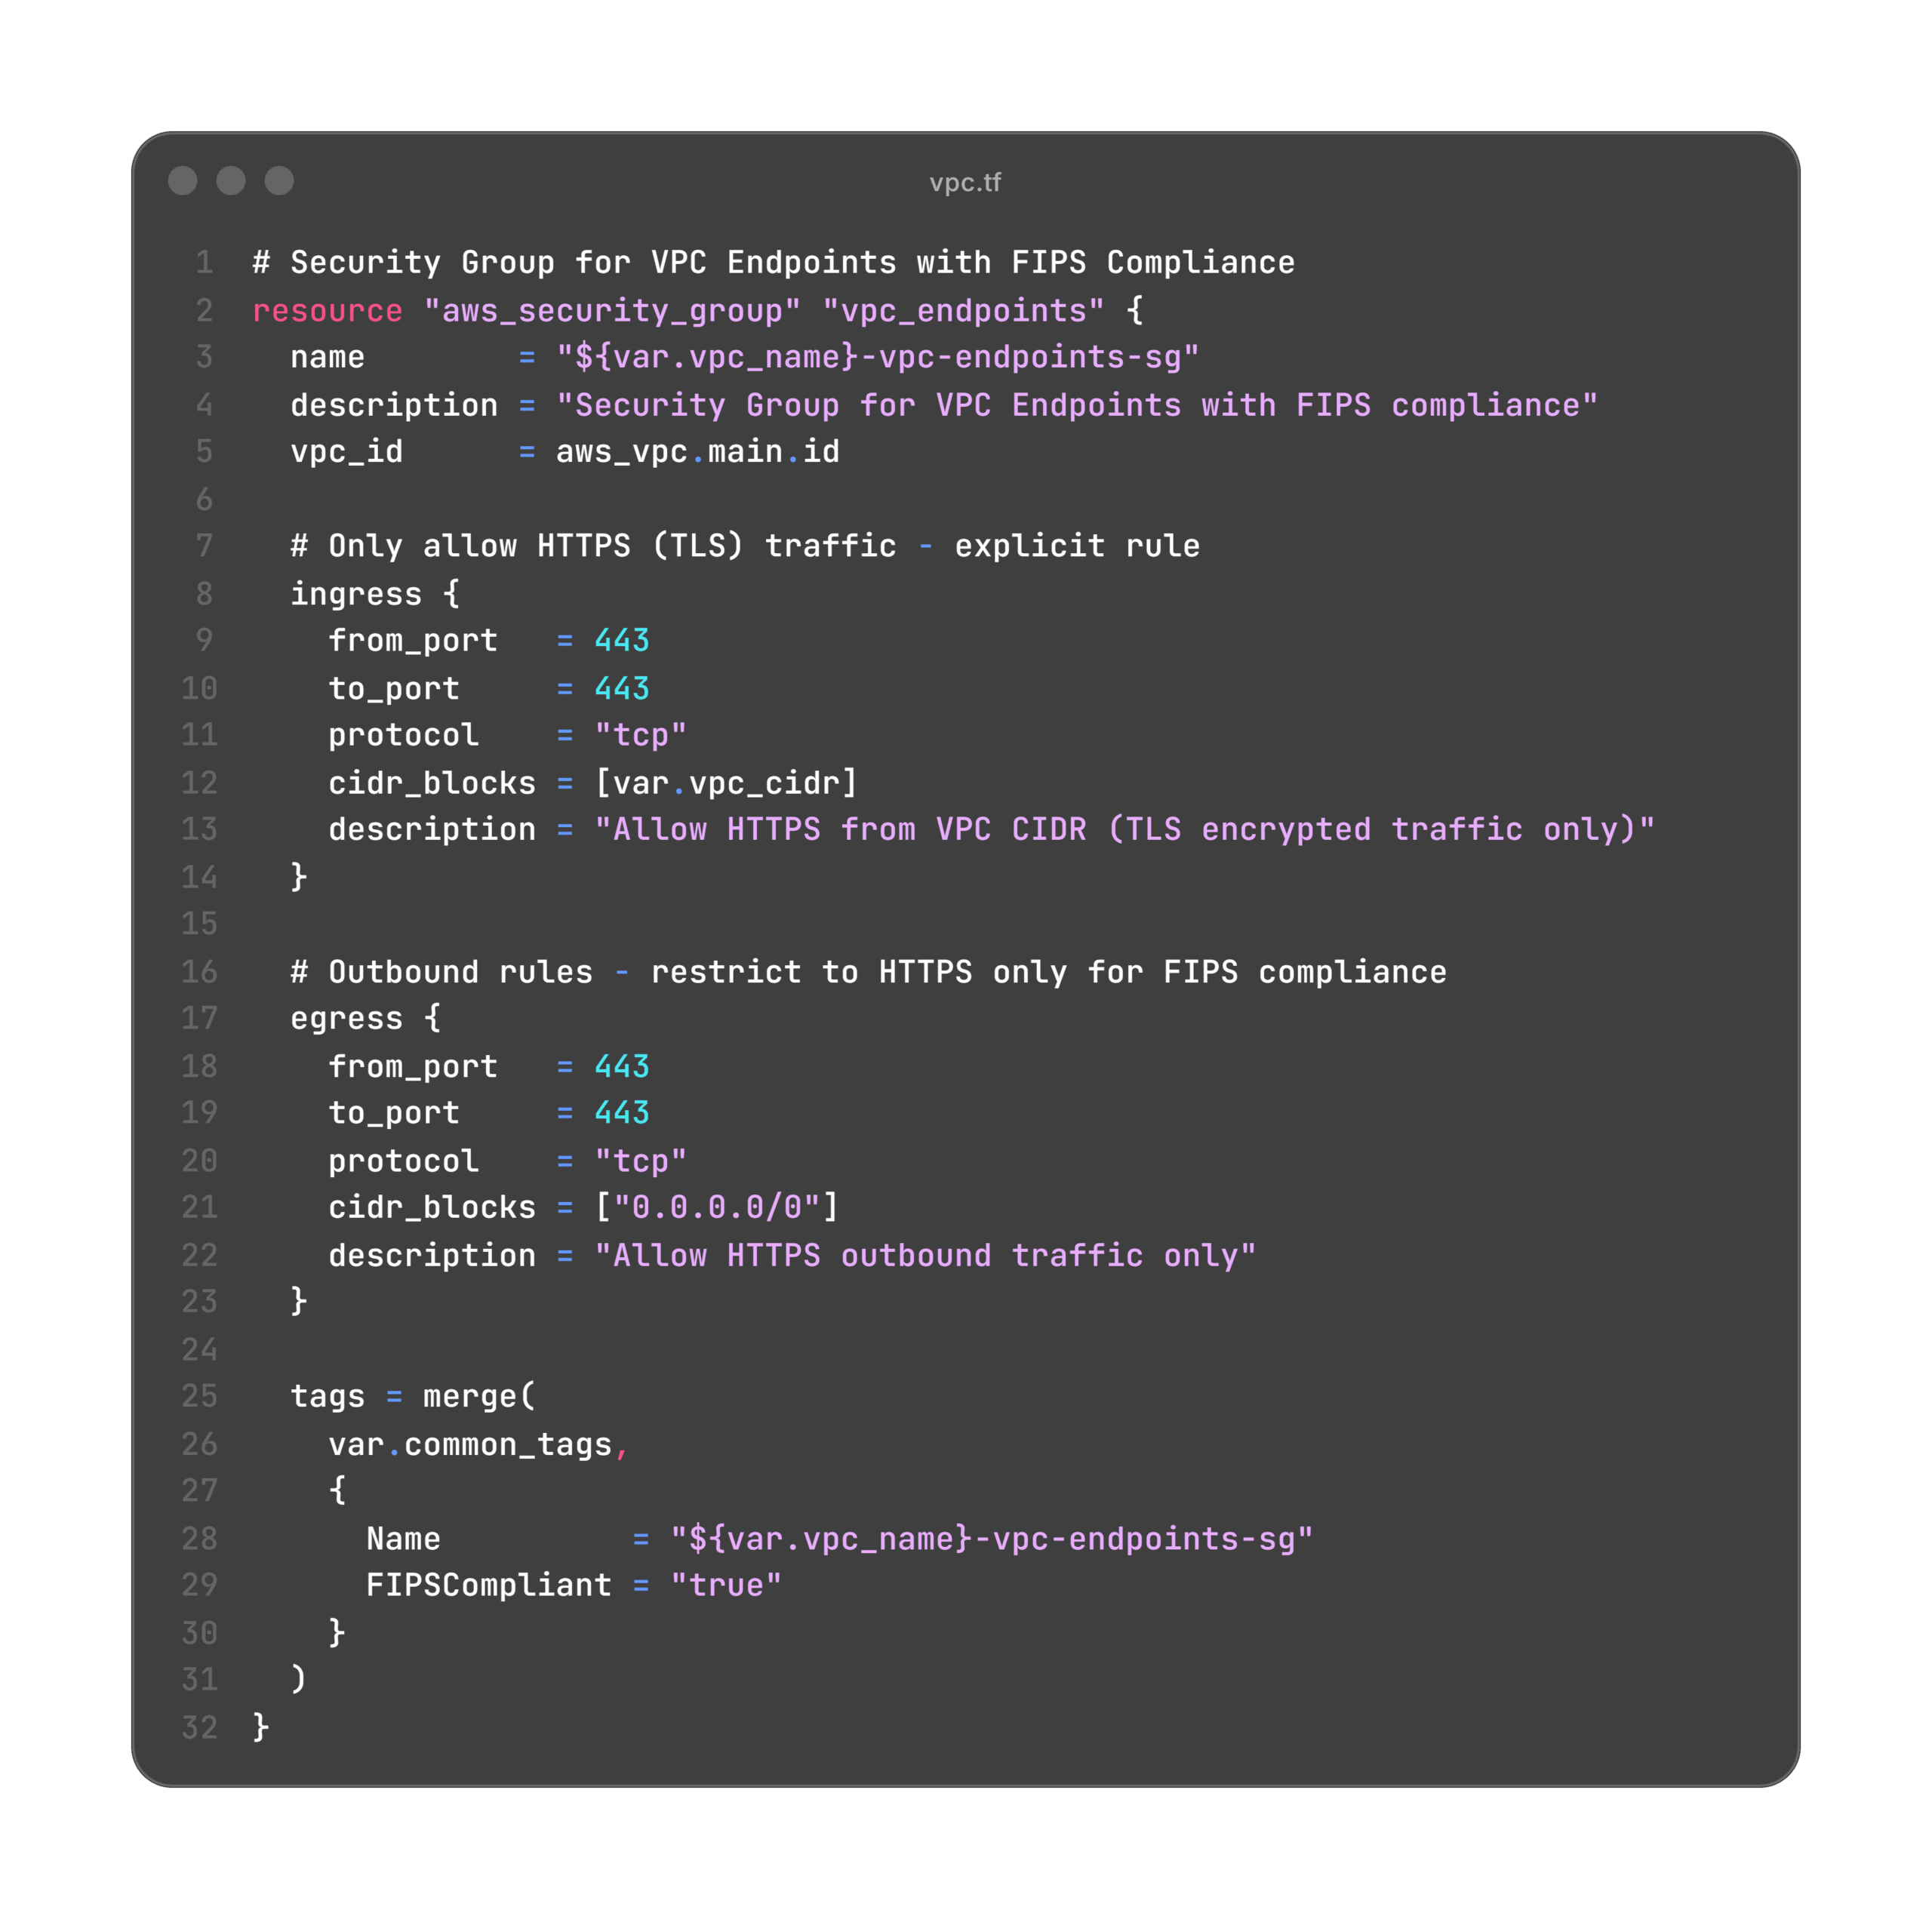
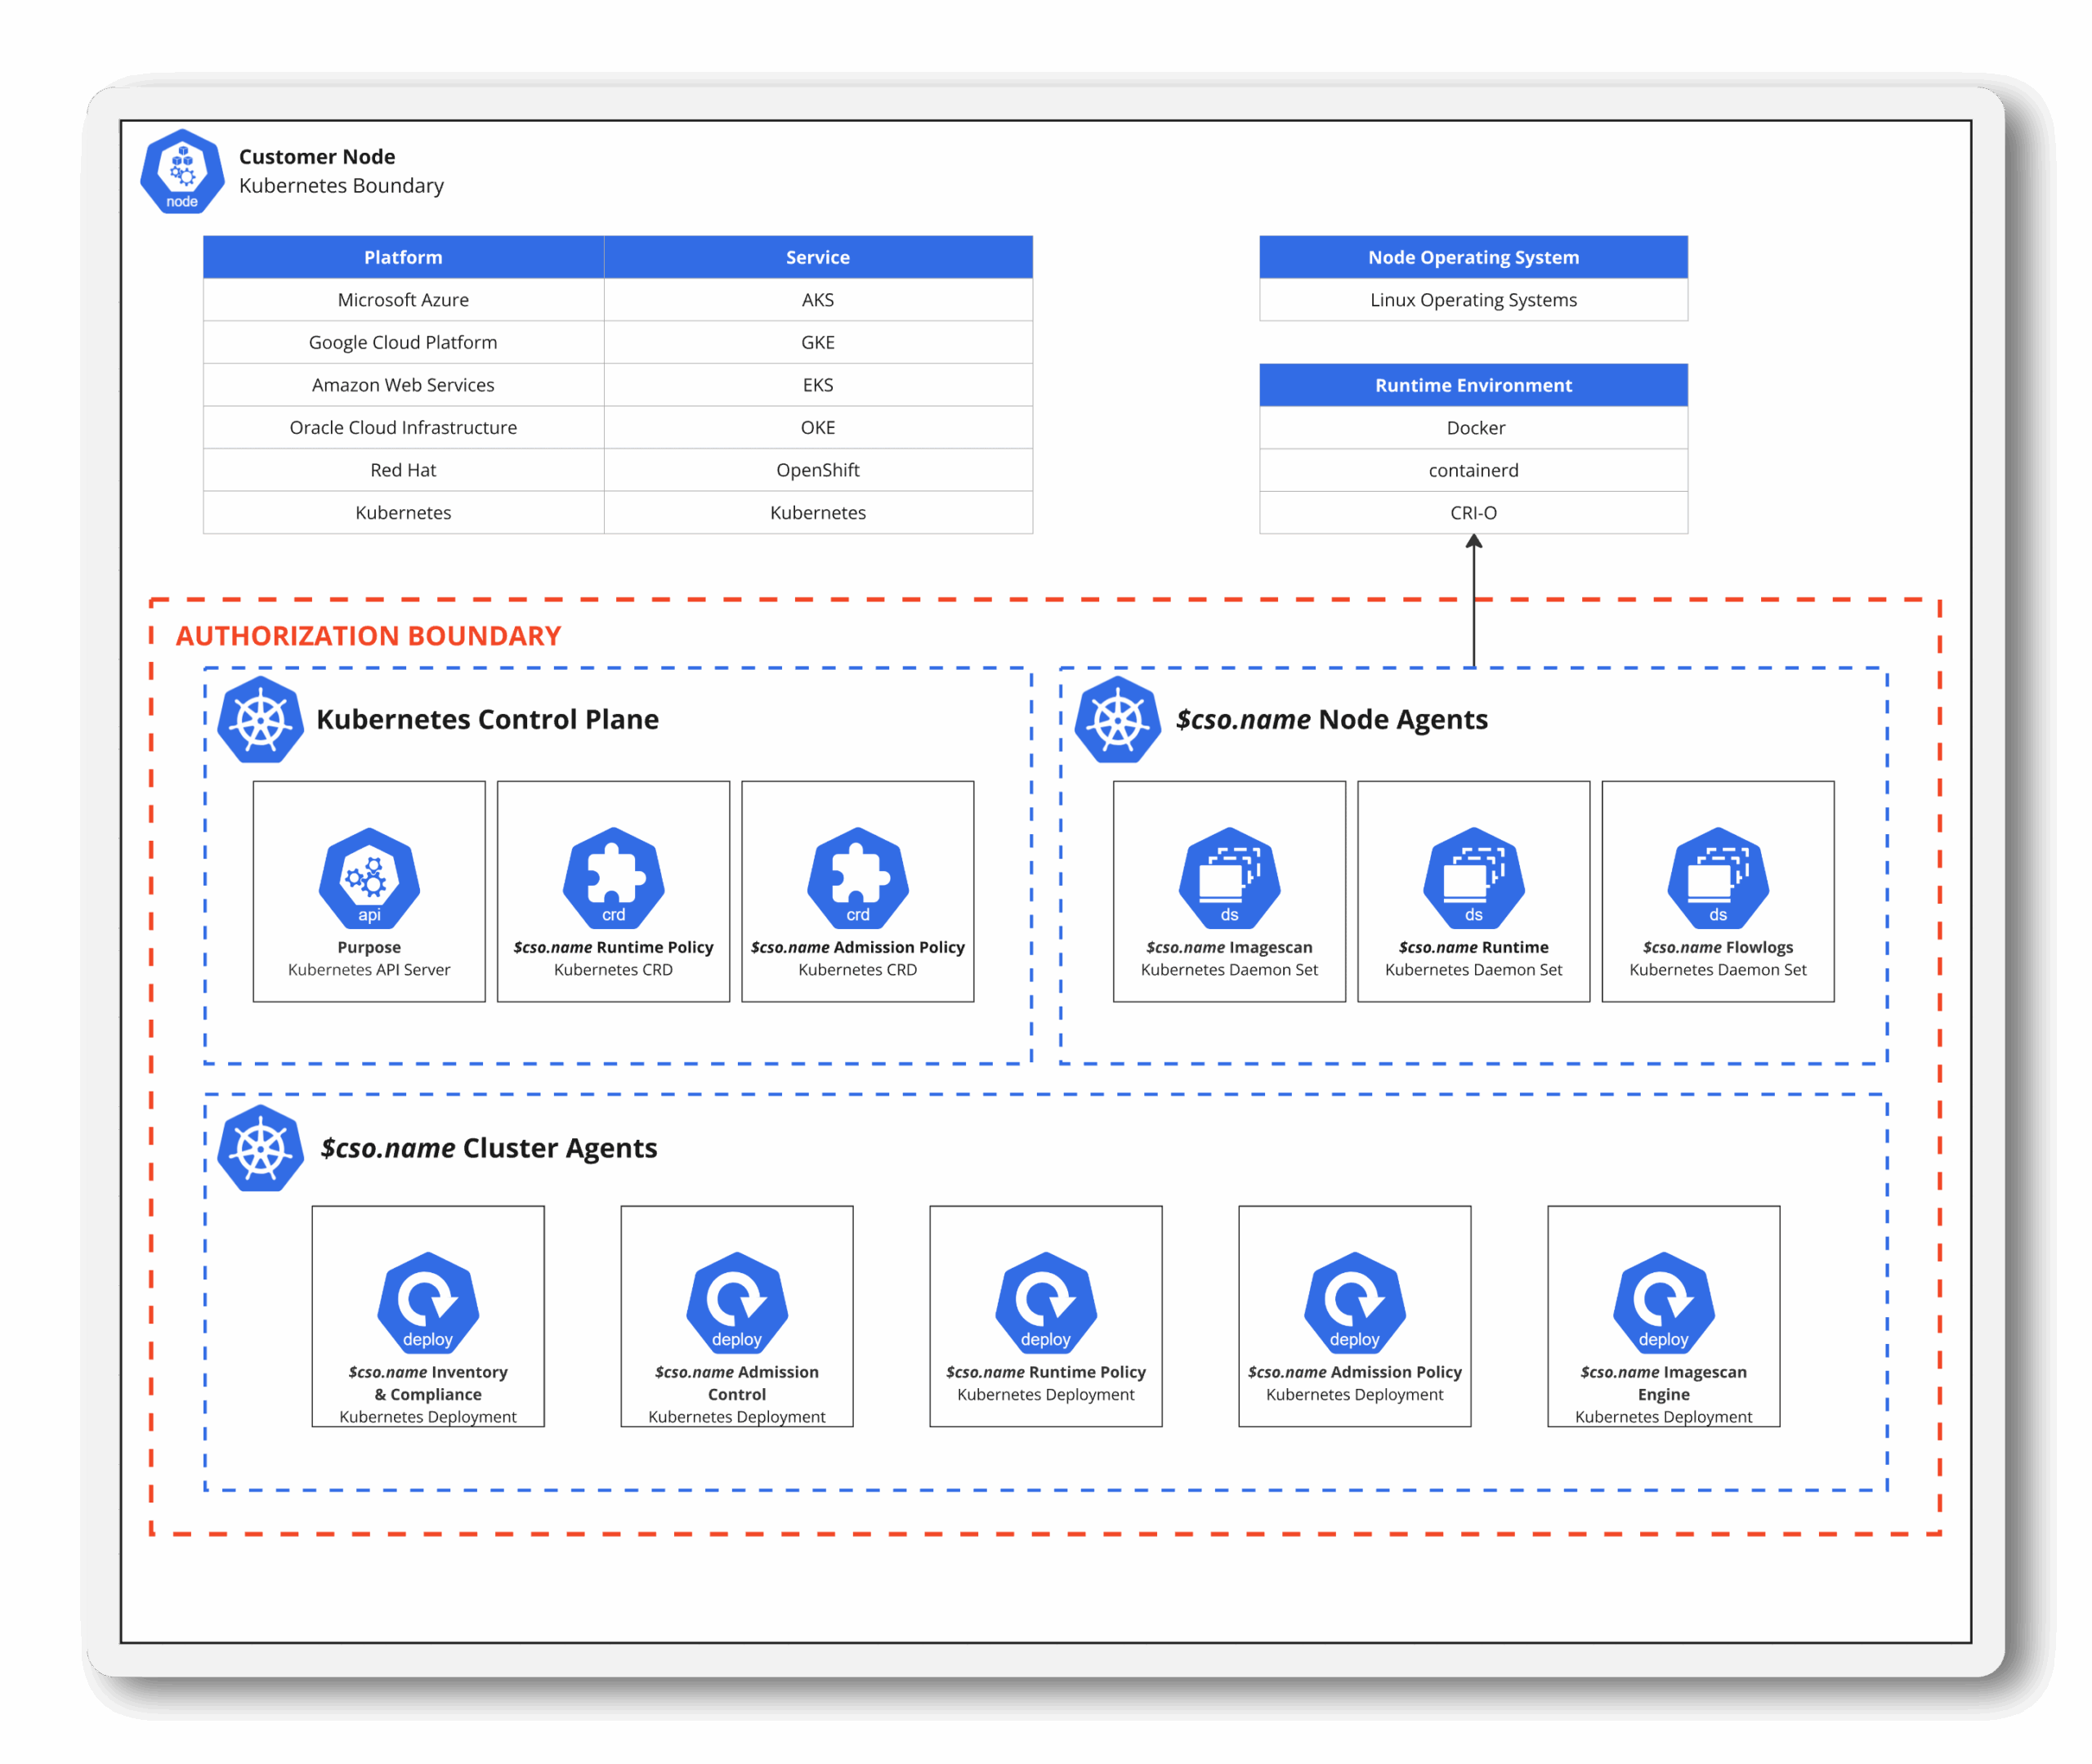
Best Results
Engineers who get your architecture
We embed with your engineering team. Our architects speak your stack, understand your CI/CD pipeline, and guide implementation so controls actually make sense for how you build.
Your Path to FedRAMP Certification
Our Battle-Tested Methodology
From gap assessment through FedRAMP Certification, we handle the technical heavy lifting and support your agency customers with their separate authorization decisions.
Gap / Discovery
We ruthlessly focus on the critical controls and showstoppers that determine your Go/No-Go decision. No theater. Just a technical roadmap.
Advisory & Build
Our team works alongside yours, guiding implementation, reviewing architecture, and keeping you on track. We develop the required certification documentation and evidence with your team, and solve the hard engineering problems.
Assessment Support
We sit on your side of the table through independent assessment and FedRAMP review. We organize evidence, explain the architecture, and support interviews and follow-up findings. We also support your agency customers with their separate authorization decisions.
Managed Services
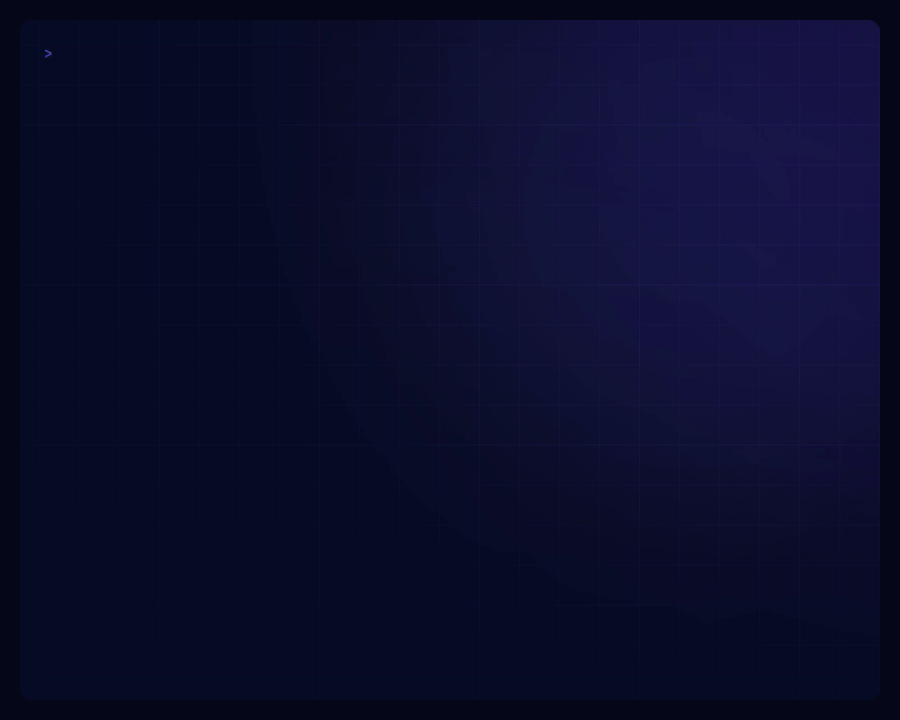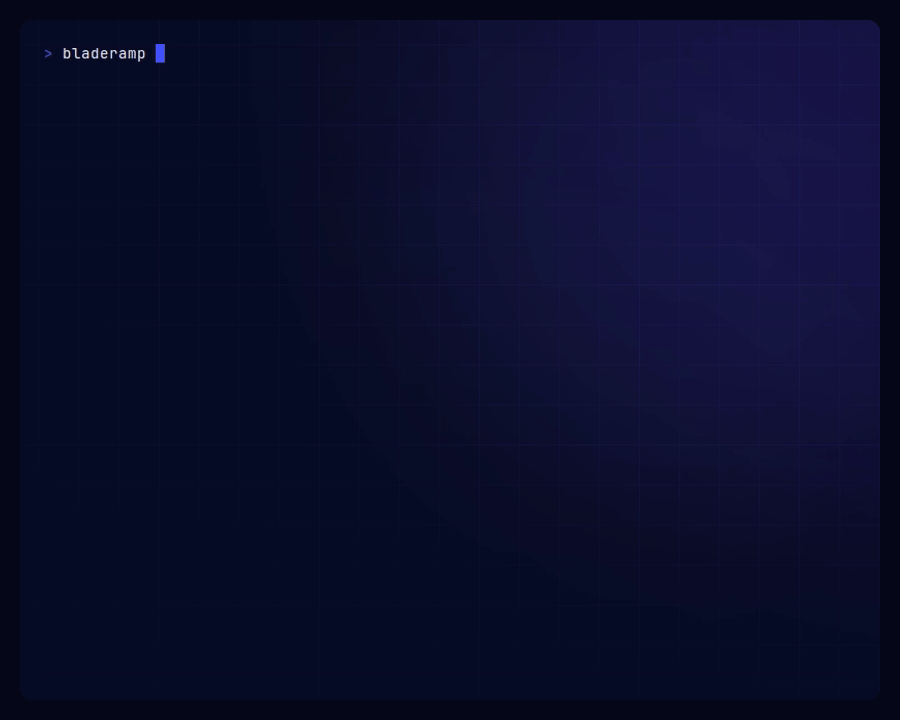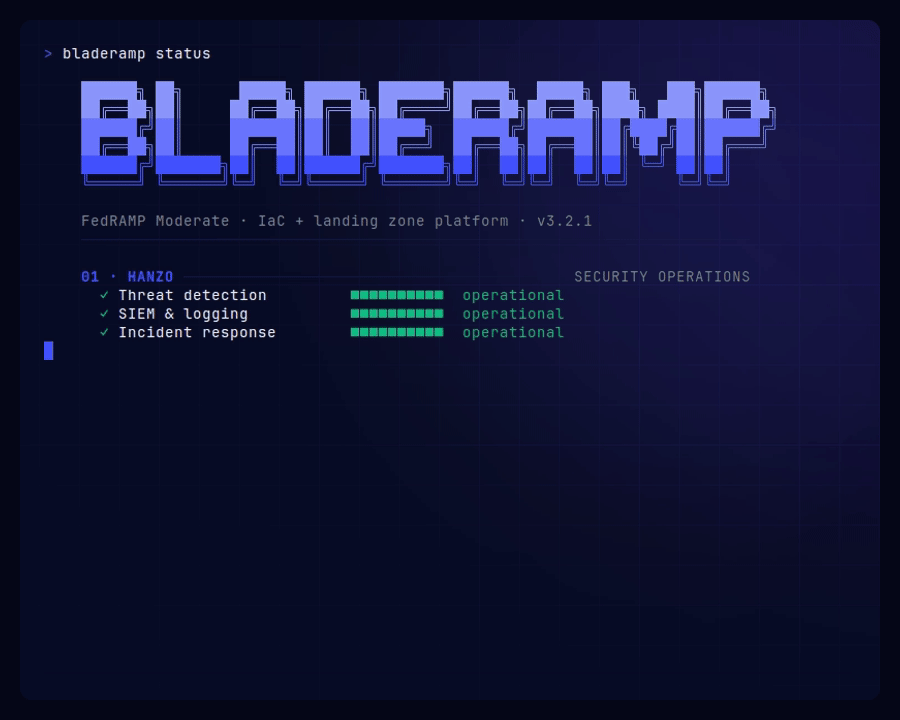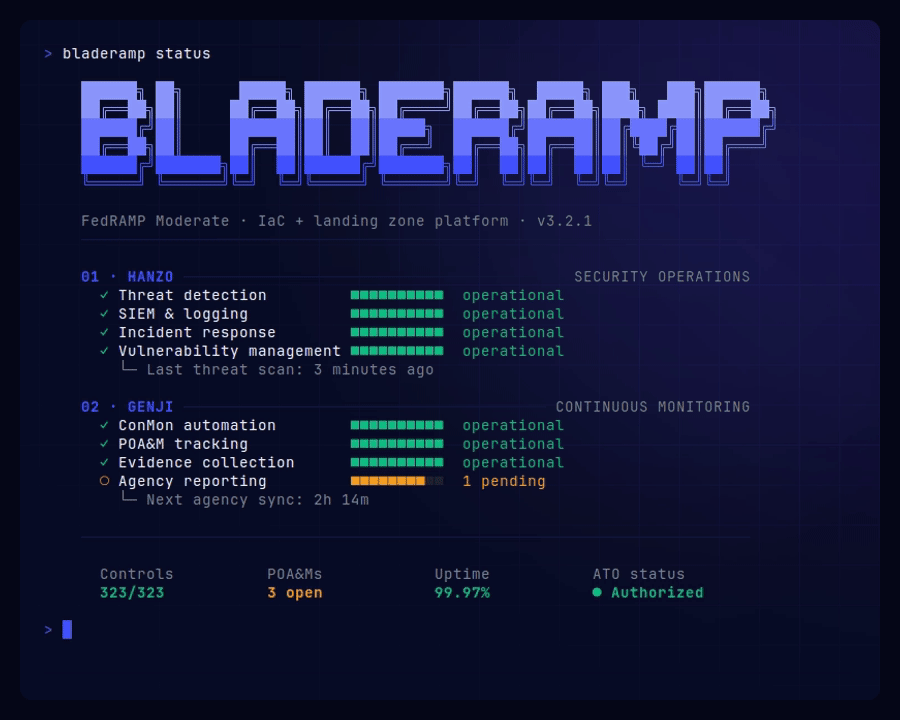
bladeRAMP:
Stay Certified.
Ongoing Certification, security operations, and vulnerability management, because certification requires maintained evidence and continued oversight.
- HANZO (SecOps)
- GENJI (ConMon)
Engagement Models
Choose your blade.
Flexible engagement models to suit your mission. From strategic advisory to fully managed platforms.
Ready to Strike?
Compliance is a task. Technical excellence is an art.
Join the ranks of the absurdly technical. Let's build your path to FedRAMP Certification and support agency adoption. Tell us about your architecture, your timeline, and your frustrations. We'll give you a practical plan.
lifecycle block, here's why."
"The organization shall implement account management procedures in accordance with organizational policy..."
Our Clients
Trusted by Leading Companies
Just some of the companies which came for the expertise. They stayed for the engineering.